

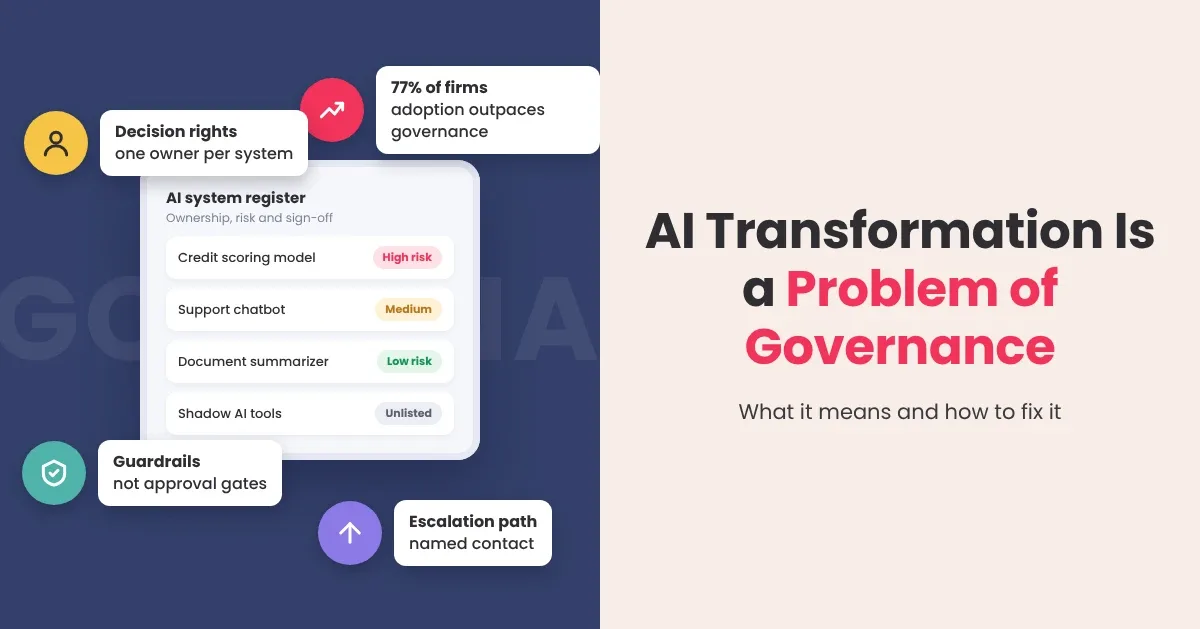
When that happens, the missing piece is rarely a better model. It is the absence of clear answers to a small set of unglamorous questions: who decides this system can go live, who owns the outcome when it is wrong, and who is allowed to switch it off.
Why AI Transformation Is a Problem of Governance?
McKinsey’s 2025 global survey found that 88% of respondents regularly use AI in at least one business function, yet nearly two-thirds said their organizations had not started scaling AI across the enterprise. Only 39% reported enterprise-level EBIT impact from AI.
That gap reveals a critical issue: AI transformation is not simply a technology problem. It is a governance problem.
Organizations can buy powerful models, deploy copilots, and build agentic AI systems quickly. The harder questions come afterward:
Who owns the AI system? What data can it access? Who approves its use? What happens when it makes a wrong decision? When should a human intervene?
An AI governance framework answers these questions by connecting responsible AI, AI accountability, risk management, compliance, data governance, and technical oversight.
Without that structure, organizations create a governance gap where AI adoption moves faster than organizational control.
What Is AI Governance and Why Do Enterprises Need It?
AI governance is the system of policies, responsibilities, decision rights, controls, and oversight models used to manage AI throughout its lifecycle.
An enterprise AI governance framework turns these principles into an operating model that determines how an organization develops, approves, deploys, monitors, and retires AI systems.
| Governance Area | Key Question |
|---|---|
| Strategy | Which AI use cases should we pursue? |
| Accountability | Who owns the outcome? |
| Data | What information can AI access? |
| Risk | What can go wrong? |
| Compliance | Which requirements apply? |
| Oversight | When must humans intervene? |
| Monitoring | How do we know AI remains reliable? |
This is where responsible AI implementation becomes practical.
A policy may prohibit employees from entering confidential information into unauthorized AI tools. Governance determines who enforces that policy, how violations are detected, and what happens afterward.
That distinction matters. Responsible AI defines the principles. Governance creates the mechanisms that enforce them.
The Challenges of AI Transformation Governance Enterprises Face
The biggest AI governance challenges appear when organizations move from isolated experiments to enterprise-wide adoption.
1. Shadow AI Creates a Governance Gap
Employees can adopt AI tools without waiting for lengthy procurement processes. This creates shadow AI: AI systems used without formal organizational approval.
IBM’s 2025 Cost of a Data Breach research found that 63% of breached organizations either lacked an AI governance policy or were still developing one. One in five organizations reported a breach involving shadow AI, while organizations with high levels of shadow AI experienced average breach costs $670,000 higher than those with low or no shadow AI.
Shadow AI is therefore more than an IT issue. It can become a security, compliance, and financial risk.
2. AI Tool Sprawl Reduces Enterprise Visibility
AI tool sprawl makes transformation oversight harder.
Marketing may use one AI platform while developers use another. Customer service may deploy an AI assistant while finance uses a separate predictive analytics system.
Without centralized governance, organizations may not know:
- Which AI systems exist
- What models they use
- What data they access
- Who owns each system
- whether required reviews are complete.
A centralized inventory and clear stewardship roles help close this visibility gap.
3. Automation Bias Can Weaken Human Judgment
AI recommendations can appear objective simply because algorithms generate them.
This creates automation bias, where employees place excessive confidence in AI outputs.
Effective ethical AI oversight requires humans to have genuine authority to question, override, or stop an AI-supported decision. A human who can only approve an AI recommendation provides limited oversight.
4. Algorithmic Accountability Changes Decision-Making
AI increasingly recommends actions, ranks decisions, and executes workflows. This creates a fundamental question:
Who is accountable when an employee follows an AI recommendation?
Clear AI accountability models and decision rights must answer that question before deployment.
Accountability cannot be assigned after an incident.
5. Regulatory Fragmentation Complicates AI Compliance
Enterprises may need to address the EU AI Act, GDPR, internal policies, contractual requirements, and sector-specific regulations.
The EU AI Act became fully applicable on August 2, 2026, subject to specific exceptions and extended transition periods for certain high-risk systems.
A governance framework can bring these requirements into common compliance structures instead of forcing every team to manage AI regulation independently.
The Core Pillars of an Enterprise AI Governance Framework
A framework is not a document you publish once. It is the set of standing answers to who decides, who owns, and who can stop each system, made operational across the AI lifecycle.
Four pillars carry most of the weight, and the reason to name them separately is that a gap in any one of them is where real incidents come from.
1. Decision Rights and Accountability
Picture a lending model that flags an application as high risk and the applicant disputes it. Who signs off that this model was allowed to make that call, who owns the error, and who had the authority to override it before it went out? If those three names are not assignable in advance, you do not have governance; you have hope.
Three questions belong in every framework before a system goes live:
- Who approves deployment at this risk level
- Who owns the outcomes when the model is wrong (a named person, not a shared inbox)
- Who can override with clear criteria for when to use that escape hatch
A lightweight decision-rights map keeps this honest.
The table below is the minimum version, using a RACI logic (Responsible, Accountable, Consulted, Informed) applied to a high-risk system.
| Decision | Accountable | Responsible | Consulted | Informed |
|---|---|---|---|---|
| Approve a system for production | Executive or AI risk committee | Product owner | CISO, Legal, Compliance | Board |
| Own model outcomes in production | Named model owner | ML/data team | Risk, Business unit lead | Executive sponsor |
| Trigger a human override or rollback | On-call model owner | Operations | Compliance | Executive sponsor |
| Sign off on audit evidence | Compliance lead | Model owner | Internal audit | Board/regulators |
Where this sits organizationally is a real choice, not a detail. A centralized model puts one team in charge of every AI decision, which is consistent but slow.
A federated model pushes ownership into business units, which is fast but drifts. A hub-and-spoke model, a small central function that sets standards while units execute, is usually the workable middle, and it maps cleanly onto P&L ownership: the unit that books the revenue from a model also owns its risk, with the CISO holding security oversight across all of them.
2. AI Risk Management and Compliance
Not every AI system requires the same controls.
An internal tool that summarizes documents presents different risks from an AI system influencing financial, employment, healthcare, or other high-impact decisions.
Effective AI risk management strategies should therefore classify systems according to their potential impact and apply proportionate controls.
The NIST AI Risk Management Framework provides a voluntary structure for managing AI risks through four core functions: Govern, Map, Measure, and Manage.
Organizations can use this alongside regulatory requirements such as the EU AI Act and GDPR.
The objective is to establish an acceptable AI risk appetite and define controls that keep exposure within that boundary. Organizations can also leverage AI governance consulting services to assess AI-related risks, establish appropriate governance controls, and align AI initiatives with regulatory and compliance requirements.
3. Technical Guardrails and Model Lifecycle Oversight
AI governance cannot stop at policy approval.
A model can perform well during testing but behave differently when its data, users, or operating environment changes.
A strong lifecycle therefore follows:
Develop → Test → Approve → Deploy → Monitor → Audit → Retire
Technical controls can include:
- Data lineage and data provenance
- Model risk management
- AI model monitoring
- Bias testing and fairness audits
- Bias mitigation
- Explainable AI
- Red-teaming
- Adversarial testing
- Access controls
- Observability
- Audit trails
- Human-in-the-Loop review
- Continuous monitoring
These controls create evidence that governance policies are actually being enforced.
For generative AI, additional risks can arise from inaccurate outputs, prompt manipulation, data leakage, and unpredictable behavior. Agentic AI introduces another layer because systems may interact directly with tools and business applications.
That makes permission controls, action monitoring, escalation paths, and human oversight increasingly important. AI SPM tools can strengthen these controls by giving security teams visibility into AI systems, the data they can access, their permissions, and risky behavior across cloud and SaaS environments.
4. Measuring AI Governance, Business Value, and Trust
Governance should not be measured by the number of policies an organization creates.
It should show whether the enterprise can scale AI while maintaining control, compliance, and business value.
| Measurement Area | Example Metric |
|---|---|
| Adoption | AI systems registered |
| Accountability | Systems with named owners |
| Risk | Systems with completed assessments |
| Compliance | Required reviews completed |
| Security | AI-related incidents |
| Auditability | Systems with audit trails |
| Monitoring | Systems under continuous monitoring |
| Business Value | Revenue or cost impact |
| Trust | User complaints and escalations |
AI audit and continuous monitoring are particularly important.
If an organization cannot determine what an AI system did, what information it used, who approved it, or why an action occurred, it becomes difficult to demonstrate accountability.
The goal is not zero risk. Every enterprise technology carries risk.
The goal is to ensure that AI risk remains within the organization's defined tolerance.
NIST AI RMF vs ISO/IEC 42001 vs the EU AI Act: Which Does What
Most pages that rank for this topic name these three in one breath and imply they are interchangeable options. They are not. One is a voluntary US framework, one is a certifiable international standard, and one is binding law with fines.
They operate at different layers, and mature programs use them together: NIST to build the taxonomy and lifecycle discipline, ISO/IEC 42001 to make it certifiable, and the EU AI Act as the legal obligation you map both onto. NIST even publishes a formal crosswalk to ISO/IEC 42001, so the work you do for one counts toward the other.
| NIST AI RMF | ISO/IEC 42001 | EU AI Act | |
|---|---|---|---|
| What it is | Voluntary risk framework (NIST AI 100-1) | Certifiable AI management system standard | Binding regulation (EU) 2024/1689 |
| Structure | Four functions: Govern, Map, Measure, Manage | Management system with roughly 38 AI-specific Annex A controls, harmonized with ISO 27001 and 9001 | Four risk tiers: unacceptable, high, limited, minimal |
| Generative/agentic AI | Generative AI Profile (NIST AI 600-1) with 12 risk categories | No GenAI annex; covered via risk and impact assessment | GPAI obligations plus Article 50 transparency duties |
| Assessment | None; self-directed | Third-party certification via a two-stage audit | Conformity assessment for high-risk (self or notified body) |
| Teeth | Voluntary, but referenced by FTC, CFPB, FDA, SEC, EEOC | Certification signals maturity to customers and partners | Fines up to 35 million euros or 7 percent of global turnover |
| Best used as | The operational spine of your program | The audit-ready wrapper around it | The compliance target you design toward |
Two corrections are worth stating plainly.
First, the EU AI Act does not govern all AI. It is risk-tiered, and most everyday enterprise use (drafting, summarizing, internal search) sits in the minimal tiers with light or no obligations. The weight falls on high-risk systems and on providers of general-purpose models.
Second, and this is where nearly every currently ranking article is now out of date: the high-risk deadline moved.
The Act entered into force on 1 August 2024, prohibited practices applied from February 2025, and general-purpose AI obligations from August 2025. Through the Digital Omnibus package negotiated in 2026, the obligations for standalone high-risk systems (Annex III) were deferred to 2 December 2027, and for AI embedded in regulated products (Annex I) to 2 August 2028.
What did not move is Article 50, the transparency duties covering chatbot disclosure, AI-content labeling, and deepfake marking, along with GPAI enforcement powers, which still land on 2 August 2026.
Governing Agentic AI: What Changes When Software Gets Decision Rights
None of the three frameworks above was built for software that acts on its own.
NIST is extending into agent-specific concerns, and a few national frameworks have started to address autonomous systems directly, but the standards you will actually cite were written for models that answer, not agents that act.
That gap matters, because an agent is not a chatbot with extra steps. A chatbot returns text a person then chooses to use. An agent takes actions: it calls tools, moves data, triggers workflows, and chains its own steps, sometimes without a human between the decision and the effect.
That shift breaks several assumptions your existing controls rest on. The controls that close the gap are concrete, and they belong in the framework as first-class scope, not afterthoughts:
- Non-human identity: Every agent needs its own identity and credentials, never a shared service account and never a borrowed human login, so that actions are attributable to a specific agent.
- Least-privilege authorization: Scope what each agent may touch to the minimum its task requires, and time-box or revoke that access when the task or pilot ends.
- Tool and action permissioning: Govern the tools an agent can call the way you govern API access, with per-action limits, so a summarizing agent cannot quietly acquire the ability to move money.
- Autonomy tiers: Define how far an agent may go before it must check with a human, and require that a person can pause or reverse a chain in flight.
- Action-level audit trails: Log what the agent did, not just what it said, so that a chain of automated steps can be reconstructed and explained after the fact.
The accountability vacuum from earlier gets sharper here, because scale and speed both increase. When agents chain steps, a small early error can cascade into a large downstream one before anyone reviews it, and attribution blurs across the agents involved.
How to Measure Whether AI Governance is Working
Ask yourself one question: if a regulator called tomorrow, could you name the owner of every model in production and the date each was last reviewed? If not, your governance is not operational yet, regardless of what the policy binder says.
Governance that cannot be measured is theater, so a framework needs a small set of metrics that are concrete, extractable, and honest about what they reveal.
The ones worth tracking, and why each matters:
- Inventory coverage: The share of AI systems (including shadow AI and agents) that are catalogued with a named owner. You cannot govern what you have not counted, so this is the base metric everything else depends on.
- High-risk sign-off rate: The percentage of high-risk systems with documented approval before production. A low number here is where regulatory exposure concentrates.
- Mean time to detect drift: How long a model runs off the rails before monitoring catches it. This is the difference between a week-two fix and a discovery during a regulatory inquiry.
- Incident MTTR: Mean time to resolve an AI incident once detected, which measures whether your escalation paths actually work under pressure.
- Human-override rate: How often humans step in on high-risk decisions, read alongside outcome quality. Zero overrides on a consequential system is a warning sign, not a success.
- Policy exception rate: How often teams route around the rules, which tells you whether the framework is usable or just ignored.
- Audit-evidence coverage: The share of decisions with a reconstructable trail, which is your real readiness for an external audit.
One honest caveat: these are directional operating metrics, not published benchmarks, so the point is the trend inside your own organization, not comparison to an industry number that does not exist yet.
A Practical Rollout: Govern Your First High-Risk System Without Boiling The Ocean
The usual advice is to write a comprehensive policy first. That is backwards.
A policy nobody has tested against a real system becomes shelfware, and the org that waits until its AI program is "big enough to justify governance" discovers that shadow AI and sprawl are already embedded while it deliberates.
Build the muscle on one system, then scale the pattern.
- Inventory everything, including shadow AI: List every AI tool, model, and agent in use across every team. The unofficial footprint is almost always larger than the official program.
- Name a single owner: Give one person or committee real authority over governance outcomes, not just projects. Shared ownership becomes no ownership the moment something breaks.
- Classify by risk: Tag each system low, medium, or high risk, so effort follows stakes instead of spreading evenly across things that do not matter.
- Instrument one high-risk system fully: Pick the system touching the most consequential decisions and build the complete stack around it: documentation, data lineage, human-in-the-loop checkpoints, monitoring, and an escalation path. This becomes your reusable template.
- Turn principles into enforceable controls: Convert each ethics commitment into a measurable control with a named owner and a defined consequence for breach. A principle without a metric is a press release.
- Set a review cadence: Governance is a living capability, so schedule recurring reviews as the regulatory picture, your model portfolio, and your risk profile all shift.
How AI Governance Applies Across Enterprise Use Cases
The governance of transformation depends heavily on context.
Financial Services
AI supporting financial decisions requires strong accountability, model governance, monitoring, and human oversight.
A system recommending a marketing offer creates different risks from one influencing a financial decision. Risk mitigation should reflect that difference.
Healthcare
Healthcare AI requires stronger attention to human oversight, data privacy, safety, explainability, and accountability.
The key question is not only whether the model performs well. Organizations must also define what happens when an AI recommendation conflicts with professional judgment.
Enterprise Operations
An internal AI assistant may summarize documents or retrieve company information.
Its governance priorities include:
- Approved data access
- User permissions
- Data privacy
- Audit trails
- Monitoring
- Clear ownership
Agentic AI
Agentic AI changes governance because systems can increasingly perform actions rather than simply generate outputs.
McKinsey found that 62% of respondents were experimenting with AI agents in 2025, while 23% reported scaling an agentic system somewhere in their organization.
| Traditional AI | Agentic AI |
|---|---|
| Produces outputs | Can take actions |
| Prompt-driven | Goal-driven |
| Limited authority | Potential system access |
| Output monitoring | Action monitoring |
This makes AI decision rights, access controls, and escalation mechanisms critical.
There is no universal governance model for transformation. Effective AI stewardship best practices reflect the organization's industry, risk profile, data environment, and operating model.
AI Governance Best Practices for Enterprise Adoption
A scalable AI governance strategy should start with visibility and accountability rather than excessive bureaucracy.
Enterprises can establish governance by:
- Inventorying AI systems across departments.
- Assigning named owners to every production AI system.
- Classifying AI risk according to business impact.
- Defining decision rights before deployment.
- Establishing AI policy and acceptable-use requirements.
- Controlling data access through data governance.
- Implementing technical guardrails across the model lifecycle.
- Testing for bias, security, and reliability before deployment.
- Maintaining audit trails and model documentation.
- Continuously monitoring AI performance and emerging risks.
This approach closes both the governance gap and the transformation gap between AI experimentation and enterprise-scale adoption.
AI Transformation Needs Governance to Scale
AI transformation does not fail simply because an organization chooses the wrong model.
It can fail because nobody owns the outcome.
It can fail because employees use unapproved AI systems. Sensitive data can reach the wrong tool. Automated decisions can become impossible to explain. An AI system can continue operating even after its risk profile changes.
These are governance problems.
An effective AI governance framework connects AI accountability, risk management, compliance structures, data governance, model governance, technical controls, human oversight, and continuous monitoring.
The objective is not to slow AI transformation.
It is to create enough control for organizations to move faster without losing accountability, trust, or visibility.
AI provides the capability. Governance determines whether an enterprise can scale it responsibly.
Frequently Asked Questions
AI transformation does not fail simply because an organization chooses the wrong model.
What is an AI governance framework?
An AI governance framework is a structured system of policies, responsibilities, decision rights, risk controls, compliance requirements, and oversight processes used to manage AI throughout its lifecycle.
Why is AI transformation a problem of governance?
AI transformation is a problem of governance because successful AI adoption requires more than working technology. Organizations also need clear ownership, decision-making authority, accountability, risk controls, and defined processes for deciding when an AI system can go live or should be switched off.
How do you implement AI governance in an enterprise?
Start by identifying AI systems, assigning owners, classifying risk, defining decision rights, establishing compliance requirements, implementing technical controls, and continuously monitoring AI performance and risk.
Why is AI governance important for AI transformation?
AI governance helps organizations scale AI without losing control over data, accountability, compliance, security, or decision-making. It turns AI adoption into a controlled enterprise capability.
What are the key pillars of AI governance?
Core pillars include AI strategy, decision rights, AI risk management, compliance, data governance, model governance, technical guardrails, human oversight, and continuous monitoring.
What is the difference between responsible AI and AI governance?
Responsible AI establishes principles such as fairness, transparency, safety, and accountability. AI governance provides the policies, roles, controls, and processes needed to apply those principles across the organization.
What tools support enterprise AI governance?h3> AI governance tools can support model monitoring, risk assessment, audit trails, data governance, red-teaming, observability, access control, and compliance management. Technology should support the governance model rather than replace it.
AI Transformation Is a Problem of Governance: What It Means and How to Fix It
AI transformation is a problem of governance because the models already work. What most companies lack is a settled answer on who owns each AI system, what it may touch and who can stop it.
The widely cited 10-20-70 rule for AI value places roughly 70% of AI value in people and processes. Algorithms account for only 10%. A 2026 survey of 2,000 technology executives found that 77% of organizations say AI adoption already outpaces their governance capabilities.
The sections below cover what the phrase claims, why pilots stall, what a 2026 enterprise AI governance framework needs and a 90-day rollout plan.
Key Takeaways
• Most AI programs stall after the pilot stage. Missing ownership, unclear decision rights or weak controls usually cause the stall, not model performance.
• Written policies fail under deadline pressure. Among large US companies in a September 2026 AI risk and governance survey, 98% have a formal policy, yet 47% have bypassed it for urgent work.
• AI agents raise the stakes because they act instead of advise. Only 21% of companies in a global study of 3,235 business leaders report a mature governance model for agents.
• Governance speeds adoption once it lives inside systems. Organizations with embedded controls report 25% fewer AI incidents.
• EU AI Act obligations for stand-alone high-risk systems now begin on 2 December 2027. Teams should use the extra time to build evidence rather than wait.
What Does "AI Transformation Is a Problem of Governance" Mean?
The statement claims that when an AI program fails to scale, the cause usually sits in the organization rather than in the code. Governance here means the decision rights, accountability structures, AI policy and controls behind every system. Together they decide how a system gets approved, who monitors it, and when it retires.
Corporate governance and risk management already do this job for finance, where boards set risk appetite while auditors check the evidence. AI governance applies the same discipline to algorithms. Algorithmic accountability sits at its core: every automated decision traces back to a person who answers for it.
The phrase also separates three jobs that companies often blur. Technology teams build the system, while management runs it day to day. Governance decides who may act on its outputs.
Without that third job, a model performs well in a demo but stalls at the first risk review. AI rarely creates these gaps on its own. An algorithm needs explicit objectives, thresholds and trade-offs, so deploying one forces leaders to settle priorities they had been able to leave vague.
Why the Phrase Keeps Showing Up on X
Thousands of monthly searches pair the phrase with "twitter" or "x.com". Many readers clearly meet it first in a post on X (formerly Twitter), then search for the argument behind it.
Posts claiming AI transformation is a problem of governance tend to appear in three kinds of conversations. Some posters push back on promises that a new tool will rescue a stalled program. Others argue that boards, rather than engineering teams, should carry AI risk. A third group applies the idea to public policy, where government AI raises the same accountability questions for citizens.
Why AI Transformation Stalls Without Governance
Adoption is no longer the hard part. A global survey on the state of AI found that 88% of respondents use AI in at least one business function. Nearly two-thirds, however, had not started scaling it across the enterprise. Only 39% reported enterprise-level EBIT impact.
Analysts describe the result as a decoupling of performance. Individual models perform brilliantly in isolation, yet enterprise-wide value fails to appear. Put simply, AI transformation is a problem of governance long before it becomes a problem of technology.
The 3,235-leader enterprise study shows where programs get stuck. Only 25% of respondents have moved 40% or more of their AI experiments into production. Most of them (84%) have not redesigned jobs around AI either. Pilots run on clean data with small teams, whereas production demands security reviews, compliance checks and a named owner for every failure.
The 2026 executive survey names the structural cause. Two-thirds of surveyed CIOs and CTOs are held accountable for AI systems they do not fully control. Seventy percent say business teams deploy technology faster than IT can track it.
Pressure from the top widens the gap. Eighty percent of those executives face CEO-driven AI mandates, yet only 11% feel fully ready for the agent deployment expected within a year.
The AI Governance Gap in 2026 Numbers
| Finding | Survey | What it tells leaders |
|---|---|---|
| 77% say AI adoption outpaces governance | 2,000 tech executives, June 2026 | Controls trail deployment by default, not by accident |
| 98% have a policy; 47% have bypassed it for urgent work | 202 AI leaders, September 2026 | A written policy is not an enforced control |
| 49% of agentic AI users have not updated their framework for agents | 202 AI leaders, September 2026 | Chatbot-era rules do not cover autonomous actions |
| 21% report a mature governance model for agents | 3,235 leaders, 2026 | Most programs are still being built |
| 74% believe they could pass an AI audit; 27% call their program fully mature | 500+ enterprise leaders, September 2026 | Confidence runs ahead of evidence |
| 36% of boards regularly discuss third-party AI risk | 500+ enterprise leaders, September 2026 | Oversight at the top is still thin |
How to Read These Surveys
The studies differ in sample size and scope, so treat them as signals pointing the same way rather than one combined dataset. The executive survey covered 2,000 technology leaders across 33 geographies in early 2026. The governance survey covered 202 senior AI decision-makers at US public companies with revenue above $1 billion, with a margin of error of seven points. The enterprise study covered 3,235 leaders in 24 countries, while the audit-readiness research covered more than 500 US enterprise leaders.
AI Governance vs AI Management
Governance and management often get used as synonyms, which is one reason accountability goes missing. Governance sets the rules, then assigns authority to enforce them. Management carries those rules out every day through testing, approvals, monitoring and incident response.
| Dimension | AI governance | AI management |
|---|---|---|
| Core question | Who decides, who owns and who can stop a system? | Is the system working as approved today? |
| Typical owner | Board, executive sponsor, AI steering committee | Product owners, ML engineers, operations teams |
| Main outputs | Policies, risk appetite, decision rights, escalation paths | Test results, monitoring alerts, change logs, incident fixes |
| Time horizon | Months to years | Hours to weeks |
Management without governance keeps systems running with nobody deciding whether they should exist. Governance without management produces policies nobody enforces.
Responsible AI sits alongside both. Its principles cover fairness, transparency and explainable AI. Governance supplies the mechanisms that make those AI ethics commitments enforceable.
Where Enterprise AI Governance Breaks Down
The biggest governance challenges appear when a company moves from isolated experiments to enterprise-wide adoption. Seven failure patterns show up repeatedly in the 2026 research.
Unclear Decision Rights
Many teams cannot say who greenlights a new use case. Nobody arbitrates when two departments want conflicting things from the same model. Legal or ethical reviews stall because no single person owns them, so projects sit in queues until the business loses interest.
Shadow AI and Tool Sprawl
Employees adopt AI tools long before procurement catches up. Data breach cost research found that 63% of breached organizations lacked an AI governance policy or were still writing one. Organizations with high levels of shadow AI paid an average of $670,000 more per breach.
Tool sprawl makes the problem worse when each department buys its own platform. Formal AI assurance reviews found shadow AI in 39% of cases, so many companies cannot list every system they would need to govern.
Accountability Without Control
A 2026 study of more than 500 enterprise leaders found that 42% of organizations give AI purchasing decisions to a single executive, usually the CIO. When one person holds the adoption decision as well as the liability exposure, risk assessment becomes harder to trust.
Policy Theater
Most large companies now have a policy, so the gap has moved to enforcement. Only 44% of organizations in the same study have documented incident response procedures for AI-specific issues. A policy that lives in a document instead of the workflow gets skipped at the first urgent deadline.
Adoption Theater
Many programs measure success by license counts or surface-level usage. Fewer than 60% of workers with sanctioned AI access use it in their daily workflow. A high adoption number can therefore hide a program delivering little value. Governance needs outcome metrics that show exactly where deployment stalls.
The Supervision Paradox
As AI tools grow more persuasive and autonomous, human oversight tends to weaken rather than strengthen. Automation bias makes recommendations look objective simply because software produced them. Reviewers who approve hundreds of outputs a day develop approval fatigue, which turns the human in the loop into a rubber stamp. Effective oversight gives reviewers the context, time and authority to halt a decision.
Regulatory Fragmentation
Ninety-four percent of surveyed organizations operate somewhere with AI rules already in effect, yet only 29% have prepared for the EU AI Act. Without a shared AI compliance structure, each team interprets regulation on its own.
What Effective AI Governance Requires
If AI transformation is a problem of governance, the fix starts with three operating habits rather than a longer policy document.

Cross-Functional Ownership
AI decisions touch business units, IT, legal, cybersecurity and HR at the same time. Leaders from each function need a seat in the process, with accountability defined before a system launches rather than after an incident.
Operational Guardrails Instead of Approval Gates
Teams move fast safely when they work from a clear rulebook. Good guardrails set boundaries on data privacy, approved tools and human-in-the-loop checkpoints. Slow bureaucratic gates, by contrast, kill useful projects without removing much risk.
Defined Escalation Paths
Employees need to know exactly whom to contact when an algorithm produces an ambiguous, biased or high-stakes output. A named contact, an agreed response time and a way to pause the system turn a worrying output into a routine fix.
The Core Pillars of an Enterprise AI Governance Framework
An AI governance framework is not a document you publish once. Think of it as a standing set of answers to who decides, who owns and who can stop each system across the AI lifecycle.
1. Decision Rights and AI Accountability
Every high-risk system needs three names before launch: the approver, the owner of its errors and the person who can override it. A lending model that flags applications as high risk is a typical case. Without those names assigned in advance, the organization has hope rather than governance.
The table below shows a minimum decision-rights map using RACI logic (Responsible, Accountable, Consulted, Informed) for a high-risk system.
| Decision | Accountable | Responsible | Consulted | Informed |
|---|---|---|---|---|
| Approve a system for production | Executive sponsor or AI risk committee | Product owner | CISO, legal, compliance | Board |
| Own model outcomes in production | Named model owner | ML or data team | Risk, business unit lead | Executive sponsor |
| Trigger an override or rollback | On-call model owner | Operations | Compliance | Executive sponsor |
| Sign off on audit evidence | Compliance lead | Model owner | Internal audit | Board or regulators |
Where this authority sits is a real design choice. A centralized model gives one team every AI decision, which is consistent but slow. A federated model pushes ownership into business units, which moves faster but drifts. Most enterprises settle on hub-and-spoke: a small central function sets standards while units execute. The unit that earns revenue from a model also owns its risk.
2. Risk Classification and AI Risk Management
Not every AI system needs the same controls. A tool that summarizes internal documents carries far less risk than one influencing credit, hiring or medical decisions. Effective AI risk management classifies systems by impact, then applies proportionate controls.
The NIST AI Risk Management Framework gives a practical structure through four functions: Govern, Map, Measure and Manage. Teams can use it to set an AI risk appetite, then define the testing each tier requires before launch. Organizations without in-house risk expertise often rely on AI governance consulting services to assess AI risks, set up controls and align projects with regulatory requirements.
3. Data Governance
Every model depends on the data it can reach. In the September 2026 survey, 72% of leaders said they worry about tracing the data lineage behind critical AI decisions. Data quality problems were the most common finding in AI assurance reviews at 57%. Good data stewardship means classifying data before connecting it, enforcing role-based access and recording where each dataset comes from.
4. Model Lifecycle Oversight
A model can pass testing, then behave differently once its data or users change. AI lifecycle governance runs through clear stages: develop, test, approve, deploy, monitor, audit and retire.

Drift is common rather than rare. Assurance reviews found model drift in 48% of cases. Among reviewed companies, 29% paused a quarter or more of their AI systems. Model risk management starts with a register of every model, version and owner. Bias testing, red-teaming, and continuous monitoring then turn that register into real oversight.
5. Human Oversight That Actually Works
Human review works when it is reserved for high-impact, hard-to-reverse actions. Requiring approval for everything produces approval fatigue, so mature programs define action tiers. Low-risk steps run automatically while medium-risk steps get logged. Anything that moves money, deletes data or changes permissions needs a person.
6. Measurement and Reporting
Governance that cannot be measured turns into theater. A short list of metrics gives leaders an honest view of whether controls work:
• Inventory coverage: the share of AI systems, including shadow AI and agents, catalogued with a named owner.
• High-risk sign-off rate: the percentage of high-risk systems with documented approval before production.
• Mean time to detect drift: how long a model runs off course before monitoring catches it.
• Incident resolution time: how quickly AI incidents are contained once detected.
• Human override rate: how often reviewers step in on high-risk decisions, read alongside outcome quality.
• Policy exception rate: how often teams route around the rules, which shows whether the framework is usable.
• Audit evidence coverage: the share of decisions with a reconstructable trail.
• Business value: revenue gained, cost saved or time recovered per governed use case.
Treat these as directional operating metrics. The trend inside your own organization matters more than comparison to an industry benchmark that does not exist yet.
Policy-Led vs Runtime-Enforced Governance
Most governance programs start with documents and review boards. The 2026 data shows why that layer alone fails. When nearly half of large companies skip their own process under pressure, the rule has to live inside the system it governs.
| Dimension | Policy-led governance | Runtime-enforced governance |
|---|---|---|
| Where rules live | Documents and review boards | Gateways, permissions and monitoring |
| Speed | Reviews slow every deployment | Checks run on every request automatically |
| Visibility | Self-reported inventories | Observed traffic and system behavior |
| Audit evidence | Assembled by hand after the fact | Logged continuously |
| Typical failure | Skipped under deadline pressure | Blocked or flagged at the point of action |
Neither layer replaces the other. Policy sets intent, whereas runtime enforcement makes it real. The 25% drop in incidents among organizations with embedded controls shows the payoff of combining them.
NIST AI RMF vs ISO/IEC 42001 vs the EU AI Act vs the OECD AI Principles
These four references often get listed together as if they were interchangeable. Each one works at a different layer. Mature programs use NIST as the operating spine with ISO/IEC 42001 as the certifiable wrapper. The EU AI Act sets the legal target, while the OECD principles supply the shared values underneath.
| | NIST AI RMF | ISO/IEC 42001 | EU AI Act | OECD AI Principles | |
|---|---|---|---|---|
| What it is | Voluntary US risk framework | Certifiable AI management system standard | Binding EU regulation (EU) 2024/1689 | Intergovernmental principles adopted in 2019, updated in 2024 |
| Structure | Govern, Map, Measure, Manage | Management system with Annex A controls | Four risk tiers: unacceptable, high, limited, minimal | Values-based principles plus policy recommendations |
| Generative AI coverage | Generative AI Profile (NIST AI 600-1) | Covered through risk and impact assessment | GPAI obligations plus transparency duties | Principles apply to all AI systems |
| Assessment | Self-directed | Third-party certification audit | Conformity assessment for high-risk systems | No assessment; guides national policy |
| Enforcement | Voluntary | Market signal to customers and partners | Fines up to €35 million or 7% of global turnover | None; shapes regulation in adhering countries |
Two clarifications matter for planning. First, the EU AI Act is risk-tiered, so everyday uses such as drafting, summarizing or internal search face light obligations or none. The heaviest duties fall on high-risk systems, along with providers of general-purpose models.
Second, the high-risk deadlines have moved. The European Parliamentary Research Service confirms that the Digital Omnibus set 2 December 2027 for stand-alone high-risk systems under Annex III. AI embedded in regulated products under Annex I follows on 2 August 2028. The Future of Privacy Forum timeline records the amending regulation's publication in the Official Journal on 24 July 2026, with entry into force on 27 July 2026.
Several obligations did not move. Prohibited practices have applied since February 2025, with general-purpose AI obligations following in August 2025. Certain content-marking duties have a grace period to 2 December 2026. Confirm exact dates with legal counsel before building a compliance plan around them.
Governing Agentic AI: What Changes When Software Can Act
A chatbot returns text that a person chooses to use. An agent calls tools, moves data or chains its own steps, sometimes with no human between the decision and its effect.
Adoption is already broad. In the September 2026 survey, 91% of senior AI executives said their organization uses agentic AI in pilots or full deployment. Among those users, 85% have systems acting without real-time human involvement, while 26% cannot detect unauthorized agents inside their own organization.
Incidents follow scale. Surveyed organizations averaged 54 AI agent incidents last year, with 17% rated high severity because containment took more than four hours. Of those serious incidents, 37% caused data exposure while 33% caused cascading system failures. Another 17% triggered compliance issues. Technology leaders expect the number of deployed agents to rise 38% by 2027.
The controls that close this gap belong in the framework as core scope:
• Non-human identity: every agent gets its own credentials, never a shared service account or a borrowed human login, so each action is attributable.
• Least-privilege access: each agent reaches only what its task requires, with access time-boxed or revoked when the task ends.
• Tool permissioning: the tools an agent may call are governed like API access, so a summarizing agent cannot quietly gain the ability to move money.
• Autonomy tiers: clear limits on how far an agent may go before it checks with a person, plus a way to pause or reverse a chain in flight.
• Action-level audit trails: logs of what the agent did, not just what it said, so a chain of automated steps can be reconstructed afterward.
Security teams can strengthen these controls with AI SPM tools, which map the AI systems running across cloud platforms or SaaS apps. They also reveal the data each system can reach, along with any risky permissions.
Board Oversight and the Chief AI Officer Role
Boards now oversee AI risk the way a board risk committee oversees financial or cyber risk, by asking for evidence rather than reassurance. Only 36% of boards regularly discuss third-party AI risk, even though AI now sits inside most SaaS tools. Enterprise research also shows that companies where senior leaders actively shape AI governance capture significantly more business value.
A workable organizational AI governance model spreads ownership without letting it dissolve:
| Role | What it owns |
|---|---|
| Board of directors | Risk appetite, oversight of high-risk AI, quarterly evidence review |
| Executive sponsor or CEO | Strategic direction and funding for the AI transformation roadmap |
| Chief AI Officer | The governance program, inventory, standards and AI steering committee |
| Chief Risk Officer | Risk classification, model risk management and escalation paths |
| CIO and CISO | Technical controls, access, security and monitoring |
| Legal and compliance | Regulatory mapping, contracts and audit readiness |
| Business unit owners | Outcomes, value and day-to-day accountability for each system |
A cross-functional AI council or steering committee ties these roles together through stakeholder alignment. The council approves high-risk use cases, settles conflicts between departments and reviews incidents. A yearly AI maturity assessment then shows the board where the program stands.
Five questions give any board a useful starting point:
• Which AI systems or agents run in production today, and who owns each one?
• What can each system access or change, plus who approved those permissions?
• How would we detect an AI tool or agent nobody approved?
• What happened in our last AI incident, and how long did containment take?
• Could we produce audit evidence for our highest-risk system this week?
Does AI Governance Slow Innovation?
Bureaucratic approval gates slow teams down, but well-designed governance has the opposite effect. Organizations with mature governance run AI agents in production at 78%, compared with 22% for those still building their programs.
Organizations that build control into their AI systems deploy 16 times more agents than those relying on manual governance. They also report 18% higher operating margins. Survey data cannot prove causation, yet the direction is consistent: teams that know the rules ship more.
The difference comes down to guardrails versus gates. Gates stop every project for review. Guardrails define pre-approved tools, data boundaries and risk tiers, so only high-impact cases wait for a human decision.
Real-World Governance Failures and What They Teach
Some of the most cited AI failures had little to do with model quality.
• Hiring: A large retailer scrapped an experimental recruiting model in 2018 after it learned to penalize résumés associated with women from historical hiring data. Bias testing before launch would have caught the problem.
• Customer service: In 2024, a Canadian tribunal held an airline liable after its website chatbot gave a passenger wrong refund information. The ruling confirmed that a company owns its AI system's answers.
• Public sector: The Dutch childcare benefits scandal saw thousands of families wrongly flagged for fraud through risk profiling. Weak oversight of automated decisions contributed to the government's resignation in 2021.
A 90-Day Rollout for Your First High-Risk System
Writing a comprehensive policy first gets the order backwards, because a policy nobody has tested against a real system becomes shelfware. Govern one system well, then scale the pattern as part of your wider change management plan.
1. Days 1 to 30, inventory everything: list every AI tool, model and agent in use, including shadow AI. Expect the first list to be incomplete.
2. Days 1 to 30, name owners and decision rights: give each system one accountable owner, then define who approves new tools, data connections or agents.
3. Days 1 to 30, classify by risk: tag systems low, medium or high so effort follows the stakes.
4. Days 31 to 60, instrument one high-risk system fully: build documentation, data lineage, human checkpoints, monitoring and an escalation path around it. Reuse that setup as your template.
5. Days 31 to 60, turn principles into controls: convert each ethics commitment into a measurable control with a named owner, plus a defined consequence for breach.
6. Days 61 to 90, test the controls: red-team for prompt injection, data leakage and tool misuse, then fix what fails.
7. Days 61 to 90, report on a cadence: give the board a one-page view of inventory, incidents and audit readiness every quarter.
Controls cost less when they are designed in from the first sprint. Our AI consulting and strategy team helps map owners, risk tiers and controls before the first build.
Which Starting Point Fits Your Organization?
The right first move depends on how far your AI program has spread, as well as how regulated your data is.
| Your situation | Start with | Why |
|---|---|---|
| Pilots only, no regulated data | Inventory and decision rights | Cheap, fast and prevents sprawl |
| Agents in production with shared tools | Runtime permissions and logging | Controls must apply on every request |
| Regulated industry or EU exposure | Risk classification and audit evidence | Evidence is the scarce asset |
| Several units deploying independently | Central registry and AI steering committee | Visibility across teams comes first |
| Mature program with high-risk agents | Continuous red-teaming and monitoring | Finds gaps that policies miss |
Governance Is What Lets AI Scale
AI transformation is a problem of governance because deployment speed now exceeds the speed of ownership, control and evidence. The 2026 surveys agree on the pattern: policies are common while enforcement is rare. Agents already act on their own inside most large companies.
Organizations that close the gap share a few habits. They count every system, name an owner for each one and classify risk before launch. They also enforce limits inside their systems, then give their boards evidence instead of reassurance. With those habits in place, governance becomes the reason AI can move faster instead of a brake on it.
Frequently Asked Questions
What does the phrase mean when people share it on Twitter or X?
On X, the line works as shorthand for a broader argument: AI programs stall from missing ownership or oversight rather than weak technology. People share it to push back on tool-first thinking. Many also use it to argue that leaders, not only engineers, must own AI risk.
Why is AI transformation considered a governance problem?
AI transformation is a problem of governance because scaling depends on questions technology cannot answer, such as who approves each system or who can switch it off. In 2026 survey data, 77% of organizations say adoption already outpaces their governance capabilities.
What is the difference between AI governance and AI management?
AI governance sets the rules, risk appetite and decision rights for an organization. AI management carries those rules out every day through testing, approvals, monitoring and incident response.
What is an AI governance framework?
An AI governance framework is a structured set of policies, roles, decision rights, risk controls and oversight processes used to manage AI across its lifecycle. Common building blocks include the NIST AI RMF, ISO/IEC 42001 and the EU AI Act's risk tiers.
Who should own AI governance in a company?
Ownership should be shared but never diffuse. The board oversees risk while a Chief AI Officer runs the program. A cross-functional steering committee approves high-risk use cases, with one accountable owner for every AI system.
Does AI governance slow down innovation?
Rigid approval gates can, but mature governance tends to speed adoption. Organizations with mature programs run AI agents in production at 78%, against 22% for those still building their programs.
How does agentic AI change governance requirements?
Agents take actions rather than produce text, so governance must cover what they do, not only what they say. Each agent needs its own identity, scoped permissions, autonomy limits and an action-level audit trail.
What does the EU AI Act delay mean for companies?
The Digital Omnibus moved obligations for stand-alone high-risk systems to 2 December 2027. Product-embedded systems follow on 2 August 2028. The duties themselves remain, so the extra time is best spent building inventories, logging and risk documentation.
Where should a company start with AI governance?
Start with a complete inventory of AI tools, models and agents, including shadow AI. Assign an accountable owner to each one, then classify systems by risk. Fully govern one high-risk system before rolling the pattern out across the business.